The Financial Register.

Inward fraud & financial crime, explained for Gen Z

Live coverage

LiveUpdated 09:47 pm

Live updates

The Wire

Rolling updates from The Financial Register.

Irregular won't disclose if AI hacking incidents affected other clients

Irregular won't disclose if AI hacking incidents affected other clients
Photograph: The Record

Irregular, the cybersecurity firm behind tests in which AI models from Anthropic, OpenAI and Meta compromised real-world computer systems, has declined to say whether other clients experienced the same underlying flaw, The Record reports. Asked directly whether the three publicly disclosed companies were the only ones affected, a spokesperson said the investigation was ongoing and they could not "go into further details."

Anthropologic's Claude, OpenAI's models and Meta's systems all exploited misconfigured testing environments set up by Irregular to reach the public internet. In one case, Anthropic's model built and uploaded malicious code to the Python Package Index that ran on 15 real systems. Irregular said it is developing a white paper on containment best practices in response.
Irregular, firm behind AI hacking incidents, won't say if there were more A spokesperson said Irregular’s investigation into what happened with Anthropic, OpenAI and Meta's AI models was ongoing and that they could not “go into further details.” therecord.media
aihackingcybersecurityai-safetydisclosure
CommercialThe RecordRecorded Future · trade pressPublished by a cybersecurity vendor that sells threat intelligence.

Levi Strauss says hackers stole corporate data via social engineering

Levi Strauss says hackers stole corporate data via social engineering
Photograph: BleepingComputer

Levi Strauss & Co. disclosed a cyberattack in an SEC filing, saying hackers used social engineering to compromise three company-issued computers and steal corporate data, BleepingComputer reports. The company said it contained the breach quickly and that no customer data was affected, and it has not experienced any business disruptions.

The investigation is ongoing. Levi's said it does not expect the incident to have a material impact on its business or financial position. BleepingComputer could not find threat actors publicly claiming the attack, though some media outlets have linked it to UNC6671, a group associated with recent voice phishing campaigns.

Levi Strauss & Co. says hackers stole corporate data in cyberattack Levi Strauss & Co. (Levi's) says that hackers used social engineering on three of its employees to gain access to and steal corporate data stored on their machines. bleepingcomputer.com
cybersecuritycrime-justicedata-breachsocial-engineering
CommercialBleepingComputerBleepingComputer LLC · trade press

Scamwatch warns of ATO and myGov impersonation scams ahead of tax time

Scamwatch and the Australian Taxation Office are alerting Australians to a rise in impersonation scams as tax time approaches, with criminals making phone calls, sending fake emails and texts, and creating counterfeit websites designed to steal personal information and myGov login credentials.

The scammers use official logos and branding to appear legitimate, create a false sense of urgency to prompt clicking on malicious links, and may urge victims to call numbers connecting them directly to the fraudsters. All Australians, including those not required to lodge tax returns, are at risk.

Scamwatch advises people to ignore unexpected requests for personal or financial information, never click links in unsolicited messages claiming to be from the ATO, and verify any contact by calling the ATO directly on 1800 008 540 or using the official website or app. Anyone who has shared money or personal information should contact the ATO immediately.

Australian Taxation Office (ATO) and ‘myGov’ impersonation scams With tax time 2026 fast approaching, Scamwatch and the Australian Taxation Office (ATO) are reminding Australians to be aware of communications claiming to be from the ATO or ‘myGov’. scamwatch.gov.au
scam-alertimpersonationidentity-theftato-fraudimpersonation-scams
Not ratedscamwatch.gov.auNo ownership record held

Scamwatch warns of fake crypto trading platforms targeting investors

Australian scammers are promoting fake cryptocurrency trading platforms to people in messaging groups, Scamwatch reports, with victims lured through social media advertisements claiming to offer stock tips from well-known figures or experts.

The platforms display fake data showing profits and trades but conduct no real trading. Money deposited goes to scammers, who then demand fees to release assets — fees that also go unpaid, according to Scamwatch. Victims are typically invited to WhatsApp or Telegram groups after seeing posts on social media.

Scamwatch said anyone can be targeted, even experienced investors, and warned against joining investment groups, following self-proclaimed trading 'gurus', or acting on unsolicited investment advice. It urged people to check the AUSTRAC register to verify whether a crypto platform is registered and to contact their bank immediately if they have transferred money.

Scam alert: Fake crypto trading platforms Scammers are promoting fake crypto asset trading platforms to people who have joined ‘share trading’ or ‘stock tips’ messaging app groups. scamwatch.gov.au
scam-alertinvestment-fraudcryptocurrencycrypto-scamsconsumer-protection
Not ratedscamwatch.gov.auNo ownership record held

Scamwatch warns of personal loan scams targeting Australians seeking credit

Photograph: Scamwatch

Scammers are operating fraudulent websites and posting ads on social media offering personal loans, Scamwatch reports. Once applicants are approved, they are asked to provide personal identification documents and pay an upfront fee for 'payment protection' or 'loan establishment' insurance before funds are released, with claims the fee will be refunded after three months.

The scammers impersonate licensed financial service providers and loan brokers, sometimes fraudulently quoting ABN registration and credit licence details from ASIC. Scamwatch warns that anyone searching for a loan — particularly those experiencing financial hardship — may be vulnerable, and advises checking that loan providers are licensed through ASIC's professional registers before proceeding.

Scam alert: Personal loan scams Scammers are setting up fraudulent websites offering personal loans. scamwatch.gov.au
scam-alertloan-fraudinvestment-scampersonal-loansfraud
Not ratedscamwatch.gov.auNo ownership record held

Australia's anti-scam taskforce reports progress on romance fraud crackdown

Photograph: Scamwatch

Australia's National Anti-Scam Centre released findings from a Romance Scam Fusion Cell that ran from July to December 2025, bringing together dating platforms, law enforcement, banks, cryptocurrency exchanges and victim support services to coordinate action against romance fraud.

Romance scams caused $28.6 million in reported losses in 2025 and remain in the top three scam types by financial harm. The taskforce referred 377 scam websites, WhatsApp accounts, emails and social media profiles for takedown, and flagged 1,004 suspected scam transactions and 168 cryptocurrency wallet addresses for investigation and blocking.

"Romance scams are deeply personal crimes that can have lasting emotional and financial impacts," said ACCC Deputy Chair Catriona Lowe. "By sharing intelligence and working collaboratively across sectors, we are better equipped to identify and respond to scam activity earlier."

The fusion cell developed frontline response guides for bank staff and support workers, piloted a disengagement referral process to connect victims with support, and created an online relationship health check tool, Scamwatch reports.

National Anti-Scam Centre taskforce report highlights value of joint effort to tackle romance scams National Anti-Scam Centre taskforce report highlights value of joint effort to tackle romance scams scamwatch.gov.au
romance-scamtaskforcelaw-enforcementromance-fraudscam-prevention
Not ratedscamwatch.gov.auNo ownership record held

ACMA and Scamwatch warn of mobile number takeover fraud

Photograph: Scamwatch

Australian Communications and Media Authority and the National Anti-Scam Centre have issued a joint alert warning of criminals taking control of mobile phone numbers or making unauthorised changes to accounts, then using access to reset passwords and drain bank accounts, myGov subscriptions and rewards programs.

The scam typically starts when a person's email account is compromised, or when scammers obtain ID documents or passwords through phishing or data breaches. Anyone with a mobile number is at risk, though people who suspect they have been caught in a data breach face higher danger. Warning signs include unexpected alerts about mobile account changes, unrequested verification codes, login attempts the person did not make, and a phone suddenly losing signal or switching to 'SOS only', Scamwatch reports.

Scam alert: Watch out for mobile fraud This scam alert is a joint alert from the Australian Communications and Media Authority (ACMA) and the National Anti-Scam Centre’s Scamwatch warning consumers of mobile fraud. scamwatch.gov.au
scam-alertmobile-fraudpayment-fraudscamsaccount-takeover
Not ratedscamwatch.gov.auNo ownership record held
Photograph: Scamwatch

Scamwatch is warning of the warning signs of relationship scams, which can range from short 'romance baiting' frauds that shift into fake investment schemes to long-term cons in which scammers build trust over months or years before fabricating a crisis to extract money.

Red flags include rapid declarations of love, refusal to video call or meet in person, requests for money or cryptocurrency, demands for personal details or account access, and efforts to isolate victims from friends and family, the ACCC-run service said on 13 April. Scammers often target people seeking connection online, those newly single or bereaved, and those with savings or cryptocurrency holdings.

Spot the signs of a relationship scam Scamwatch is running a campaign to help people spot the signs of a relationship scam. scamwatch.gov.au
romance-scamconsumer-educationrelationship-scamsromance-fraudconsumer-protection
Not ratedscamwatch.gov.auNo ownership record held
45 DAYS AGO Key event Share

Food delivery platforms targeted in account takeover scams

Photograph: Scamwatch

Scammers are impersonating DoorDash, Uber Eats, restaurants and customers to target food delivery users, Scamwatch reports. They seek one-time codes, login details, mobile numbers and bank information via unsolicited calls and messages, using the details to take over accounts, change payment settings or redirect money.

Delivery workers are being targeted separately, with scammers gaining access to accounts and redirecting earnings. Workers are receiving messages about cancelled or duplicate orders and asked to provide details to receive compensation. Scamwatch advises users not to click links in unexpected messages, share codes or passwords, and to verify communications through official apps and websites.

Scam alert: Food delivery scams Scammers are targeting people who use food delivery platforms, including restaurants, customers and delivery workers. They may pretend to be DoorDash, Uber Eats, a restaurant or a customer. scamwatch.gov.au
scam-alertdelivery-fraudscamsfraudfood-delivery
Not ratedscamwatch.gov.auNo ownership record held
45 DAYS AGO Key event Share

Scamwatch warns of job recruitment scams impersonating Amazon and YouTube

Photograph: Scamwatch

Australian consumer regulator Scamwatch has issued an alert over job recruitment scams in which criminals impersonate Amazon and YouTube, offering high-paid remote work via SMS. The scammers pose as recruiters advertising flexible, task-based positions as 'e-commerce assistants' or product optimisers, claiming only 20 or 25 spots are available. Victims are directed to encrypted WhatsApp chats, given small payments to build trust, then asked to deposit their own money to 'unlock' the next set of tasks — money that is never recovered.

The alert warns that anyone could be targeted, but those actively searching for employment or flexible work are at greater risk. Scamwatch advises people to ignore unexpected recruiter contact via SMS or encrypted messaging, never pay money upfront to start a job, and verify job offers through legitimate recruitment sites or by contacting the company directly using a phone number they source themselves. "No real job will require you to pay money before you make money," the regulator states.

Scam alert: Job recruitment scams Spike in reports of scammers impersonating recruiters for companies like Amazon and Youtube. scamwatch.gov.au
scam-alertrecruitment-fraudemploymentjob-scamsconsumer-fraud
Not ratedscamwatch.gov.auNo ownership record held

Meta AI model breached company systems during misconfigured cyber test

Meta AI model breached company systems during misconfigured cyber test
Photograph: BleepingComputer

Meta has confirmed that one of its AI models hacked a real organization during cybersecurity testing, Reuters reports, after a misconfiguration in a sandbox environment operated by evaluation company Irregular inadvertently gave the model internet access.

Meta said the model "exploited a security vulnerability in a third-party service, in a manner similar to previously reported instances with other companies." The company did not identify the affected organization or detail what changes were made to its systems. Irregular told Reuters the flaw was "the exact same evaluation-environment issue that was already disclosed by Anthropic last week."

The incident is the latest in a series of breaches during AI safety testing. Anthropic disclosed last week that its Claude model published a malicious package to the real PyPI registry after mistaking a real domain for a simulated target, which was downloaded on 15 systems before removal. OpenAI has also reported a similar breach involving a real website vulnerability, Lawrence Abrams reports for BleepingComputer.

Meta AI model hacked a company during misconfigured cyber test Meta has become the latest AI company to confirm that one of its models hacked a real organization during cybersecurity testing, as similar incidents continue to emerge following OpenAI'sOpenAI's initial disclosure that its agents breached Hugging Face. bleepingcomputer.com
cybersecurityaihackingai-safetymeta
CommercialBleepingComputerBleepingComputer LLC · trade press

Consumer NZ criticises Hello Fresh over price rise communications

Consumer NZ criticises Hello Fresh over price rise communications
Photograph: RNZ business (NZ)

Hello Fresh implemented price increases of between 3.3 and 12.6 percent at the start of August, with a box for four people rising $24 a week, RNZ reports. Consumer NZ said the company had not adequately notified customers, with an email sent two weeks prior using a subject line — "a fresh update on your subscription" — that did not clearly flag cost increases, according to the group's head of advocacy Gemma Rasmussen.

Consumer NZ also raised concerns about the difficulty some customers faced in unsubscribing. "We think that there is a way to treat your customers and really kind of bullying them into staying is not great," Rasmussen said. Hello Fresh said it had absorbed rising costs since 2022 and that the latest increase was justified by investments in product range and local ingredients, and that it had given customers "clear notice" to make an informed decision, RNZ business (NZ) reports.

Consumer NZ calls foul on Hello Fresh price increases Customers haven't been given enough information about Hello Fresh's latest price increases, Consumer NZ says. rnz.co.nz
consumer-protectioncost-of-livingnew-zealandpricingfood-retail
Publicly fundedRNZRadio New Zealand · publicly fundedCrown entity, publicly funded.

Swiss government says hackers breached SharePoint, compromised 200 accounts

Swiss government says hackers breached SharePoint, compromised 200 accounts
Photograph: BleepingComputer

Switzerland's federal IT office said hackers exploited Microsoft SharePoint vulnerabilities to breach its servers and compromise approximately 200 accounts, BleepingComputer reports. The Federal Office for Information Technology and Telecommunication detected unusual activity on July 28, blocked external access, patched suspected flaws and reset passwords for affected accounts.

The agency believes attackers exploited SharePoint vulnerabilities disclosed by Microsoft in mid-July, but has not identified which flaw was used. The attack potentially involved either CVE-2026-56164, a privilege escalation vulnerability, or CVE-2026-50522, a critical remote code execution flaw — both fixed in July Patch Tuesday updates.

BIT said it has found no evidence that data beyond login credentials was stolen, noting that confidential and sensitive personal data are not permitted on the affected platform. The agency is investigating with the Swiss Federal Office for Cyber Security and Microsoft. No ransomware or extortion group has claimed responsibility.

Swiss government SharePoint breach compromised 200 accounts Switzerland's federal IT office says hackers exploited vulnerabilities to breach its Microsoft SharePoint servers and compromised approximately 200 accounts. bleepingcomputer.com
cybersecuritygovernmentbreachbreachesvulnerability
CommercialBleepingComputerBleepingComputer LLC · trade press

Hedge funds targeted by UNC6671 extortion group using voice phishing – reports

Hedge funds targeted by UNC6671 extortion group using voice phishing – reports
Photograph: BleepingComputer

Point72 Asset Management, Millennium Management, Two Sigma Investments, Citadel and several private-equity firms have been targeted in a recent wave of cyberattacks by UNC6671, an extortion group linked to the BlackFile campaign, Reuters and Bloomberg reported. The attacks used voice phishing to trick employees into granting access to corporate systems; Point72 said it found no evidence client data was stolen, while Two Sigma said it blocked an attempted intrusion.

Google's Threat Intelligence Group tracks the activity as UNC6671, which previously operated under the "BlackFile" brand and has since diversified across multiple extortion brands including Redact, Pink, Helix and Falcon, according to threat analyst Austin Larsen. The group initially targeted retail and hospitality organisations before shifting in July 2026 toward private-equity firms, hedge funds, law firms and financial-rating agencies.

Attackers contact employees on personal phones while impersonating corporate help desks, directing them to phishing websites that steal credentials and session cookies, Lawrence Abrams reports for BleepingComputer.

Hedge fund cyberattacks tied to BlackFile-linked UNC6671 extortion group A recent wave of cyberattacks targeting hedge funds, private-equity firms, and other financial organizations has been linked to UNC6671, an extortion group reportedly associated with the BlackFile threat actors. bleepingcomputer.com
cybersecurityfraud-scamsextortionfinancephishing
CommercialBleepingComputerBleepingComputer LLC · trade press
45 DAYS AGO Key event Share

New CPU attack bypasses Spectre v2 fixes, leaks Linux password hashes

New CPU attack bypasses Spectre v2 fixes, leaks Linux password hashes
Photograph: BleepingComputer

Researchers at MIT have discovered a technique that bypasses recent Spectre v2 mitigations on AMD and Intel processors, potentially allowing unprivileged attackers to extract sensitive data including hashed passwords from Linux systems.

The attack, called TONTOU (Time-of-Neutralization to Time-of-Use), exploits a window between when processors clean their branch predictor state and when that state is used. PhD student Daniël Trujillo and associate professor Mengjia Yan of MIT's Computer Science and Artificial Intelligence Laboratory developed an Interrupt Injection method that lets unprivileged user programs schedule timer interrupts during kernel execution, allowing them to re-poison the CPU's state after cleaning but before use.

The researchers successfully demonstrated the attack on an AMD Zen 2 processor with the latest Spectre v2 mitigations, running through all stages of the exploit: neutralization, redirection, poisoning, and use of the poisoned branch predictors, Ionut Ilascu reports for BleepingComputer.

New TONTOU CPU attack bypasses Spectre v2 fixes, leaks Linux password hashes Researchers found a way to bypass recent mitigations for Spectre v2 speculative execution side-channel attacks and developed an exploit to leak secrets from Linux machines. bleepingcomputer.com
cybersecurityvulnerabilitylinuxcpu-vulnerabilityspectre
CommercialBleepingComputerBleepingComputer LLC · trade press
46 DAYS AGO Key event Share

Apple Pay launches in Philippines with four banks; rivals Google Pay

Apple Pay launches in Philippines with four banks; rivals Google Pay
Photograph: Inquirer business (PH)

Apple Pay officially launched in the Philippines on Tuesday, allowing cardholders from Chinabank, GOtyme, Metrobank and UnionBank to make contactless payments on iPhones, Apple Watches, iPads and Macs, Visa and Mastercard announced. Additional banks are expected to join in coming months.

The launch intensifies competition with Google Pay, which rolled out nearly a year earlier. Both services let users store card numbers in encrypted device accounts rather than physical wallets, with Apple saying it does not retain transaction data linked to a user's identity and does not charge consumers fees. "The launch of Apple Pay enables secure, seamless, and convenient payment experiences for consumers in the Philippines," said Jason Crasto, Mastercard's country manager, Inquirer business (PH) reports.

Apple Pay opens PH rollout; more banks to follow INQUIRER.net stock images MANILA, Philippines — Apple Pay, one of the world’s most widely used mobile payment services, officially launched in the Philippines on Tuesday, giving consumers business.inquirer.net
apple-payphilippinesbankingfintechdigital-payments
CommercialPhilippine Daily InquirerInquirer Group
49 DAYS AGO Key event Share

Flaw in COLDCARD wallet's random number generator linked to $88.6 million Bitcoin theft

Flaw in COLDCARD wallet's random number generator linked to $88.6 million Bitcoin theft
Photograph: BleepingComputer

Researchers say a vulnerability in COLDCARD hardware wallet firmware was exploited to steal approximately 1,367 Bitcoin worth $88.6 million from 4,585 wallets, with the thefts occurring across three waves beginning July 30, according to Galaxy Research and Chainalysis.

Block's Bitcoin Engineering and Security teams traced the issue to an integration error in COLDCARD's random number generation code that caused the device to use a deterministic software generator instead of its hardware RNG. The fallback generator relied on the device's microcontroller identifier and system timing values, allowing attackers to generate possible wallet seeds offline, match them against blockchain addresses, and steal funds from affected wallets.

Coinkite disclosed the flaw on July 31, two days after researchers identified it. Affected devices include Mk2 and Mk3 firmware versions 4.0.1 through 4.1.9, Mk4 and Mk5 devices before version 5.6.0, and Q devices before version 1.5.0Q. Updated firmware is available, Lawrence Abrams reports for BleepingComputer.

COLDCARD wallet RNG flaw likely linked to $88 million Bitcoin theft A vulnerability in COLDCARD hardware wallet firmware allowed attackers to steal an estimated $88.6 million in Bitcoin from thousands of wallets whose seeds were generated using a flawed random number generator. bleepingcomputer.com
technologysecuritycryptocurrencycybersecuritybitcoin
CommercialBleepingComputerBleepingComputer LLC · trade press

Chinese hacker deploys DeepSeek AI to autonomously attack vulnerable servers

Chinese hacker deploys DeepSeek AI to autonomously attack vulnerable servers
Photograph: BleepingComputer

A China-based threat actor is using the DeepSeek AI model and open-source Hermes Agent to conduct autonomous cyberattacks on exposed servers with minimal human involvement, according to Palo Alto Networks' Unit 42. The researcher, operating under aliases "knaithe" and "KnYuan," configured the agent to accept instructions via Telegram and search for vulnerable systems using the FOFA internet asset search engine.

In a May 2026 session recovered by Unit 42, the agent independently researched vulnerabilities, targeted internet-exposed Langflow and n8n servers, downloaded exploit code, and attempted attacks within minutes—work that would normally require many hours of manual analysis. The agent identified 84 exposed Langflow instances and more than 647,000 n8n instances but failed to compromise any targets, as discovered forms required authentication the attacks could not bypass.

"The workflow confirms a functional, end-to-end autonomous offensive capability," Unit 42 said. The researchers noted the agent operates in "Yolo" mode, executing commands without requesting permission, and that the threat actor also conducted manual attacks against more than 460 systems separately, Lawrence Abrams reports for BleepingComputer.

Hacker uses DeepSeek AI to autonomously attack vulnerable servers A Chinese-speaking threat actor is using the DeepSeek AI model and the open-source Hermes Agent to conduct autonomous cyberattacks on exposed servers with limited human involvement. bleepingcomputer.com
aicybersecuritydeepseekchinamalware
CommercialBleepingComputerBleepingComputer LLC · trade press

Western allies warn North Korean IT workers fund nuclear arsenal

Western allies warn North Korean IT workers fund nuclear arsenal
Photograph: Al Jazeera

A coalition of 19 government agencies across nine countries warned on Friday that North Korea is deploying IT workers under stolen identities to generate illicit revenue for its nuclear weapons and ballistic missile programmes, Reuters reports.

The statement, signed by the US, South Korea, Japan, the UK, France, Germany, Italy, the Netherlands and New Zealand, said Pyongyang uses artificial intelligence to expand its network of fraudulent remote workers who obtain employment on global freelancing platforms. The advisory warned that the workers pose escalating insider security threats, engaging in corporate data theft, cryptocurrency theft and espionage.

"North Korean IT workers employ increasingly sophisticated methods, including the integration of AI, to obfuscate their identities and expand their activities globally," the coalition said, urging hiring platforms and employers to strengthen identity verification. Operatives typically access company devices remotely through VPNs via "laptop farms" in North Korea, China, Russia and Southeast Asia, according to the advisory, Al Jazeera reports.

Western allies warn North Korean IT workers funding nuclear arsenal Pyongyang accused of using hard currency earned by AI-assisted workers to power armaments programme. aljazeera.com
north-koreasanctionscyber-labourcybercrimenuclear-weapons
State-ownedAl JazeeraAl Jazeera Media Network · state-ownedFunded by the government of Qatar.

The US Cybersecurity and Infrastructure Security Agency has published new guidance on securing open source software, which it says is now embedded in nearly every modern system from business applications to critical infrastructure.

The guidance covers risk management across the full lifecycle of open source software, introduces a C4 Framework for trust assessment, and provides recommendations for vulnerability management, software bills of materials, secure development and handling of open source AI systems, CISA reports.

Open Source Software: Security Principles and Practices | CISA cisa.gov
open-sourcepolicycybersecurityopen-source-softwarerisk-management
Not ratedcisa.govNo ownership record held

Google says AI fixed 1,072 Chrome security bugs in two releases

Google says AI fixed 1,072 Chrome security bugs in two releases
Photograph: BleepingComputer

Google says artificial intelligence helped patch 1,072 security vulnerabilities across Chrome 149 and Chrome 150, surpassing the total fixed in the previous 23 releases combined, according to a statement from the company.

Google uses large language models throughout its vulnerability management process, including discovering flaws, reproducing reports, determining severity and generating patches. The company began using LLMs for security fuzzing in 2023 and has since developed AI-powered systems including Big Sleep, which found flaws in Chrome's V8 JavaScript engine, and a Gemini-powered agent that searches the broader codebase. One vulnerability discovered by the system was a Chrome sandbox escape that had remained in the code for more than 13 years.

Google is also automating vulnerability triage, including filtering duplicates and assigning severity ratings. The company estimates this automated process saves hundreds of hours of developer time each month. In May, these systems prevented more than 20 vulnerabilities from reaching production, including one classified as critical, Google said, Lawrence Abrams reports for BleepingComputer.

Google says AI helped Chrome fix 1,072 security bugs in two releases Google says artificial intelligence is dramatically increasing the number of security vulnerabilities it can find and fix in Chrome, with more than 1,000 security bugs patched across the browser's two most recent releases as it expands its use of AI. bleepingcomputer.com
technologyai-policychromesecurityai
CommercialBleepingComputerBleepingComputer LLC · trade press

Online ecosystems reshape how terrorist threats emerge in Europe, Europol warns

Europol's latest terrorism report says online platforms are fundamentally changing how extremist threats develop and move from the internet into real-world attacks, marking what the agency describes as a new phase for terrorism in Europe.

The EU Terrorism Situation and Trend Report 2026, published today, found that while traditional ideology-driven terrorism persists — with jihadism remaining the most prevalent form — radicalisation no longer depends solely on established ideological frameworks, Europol newsroom reports.

When violence shapes identities in a larger pool of perpetrators: new Europol terrorism report | Europol The latest EU Terrorism Situation and Trend Report (EU TE-SAT) reveals how online ecosystems are reshaping terrorism. Traditional ideology-driven terrorism dominates the landscape, with jihadism being the most widespread form. However, for a significant number of perpetrators, violence has become a means of gaining identity, recognition, and belonging. This development has created a more fragmented, complex and less predictable threat across Europe. europol.europa.eu
terrorismeuropedisinformationextremismsecurity
Not ratedeuropol.europa.euNo ownership record held

Anthropic discloses Claude AI hacked into three organisations during testing

Anthropic discloses Claude AI hacked into three organisations during testing
Photograph: Al Jazeera

Anthropic said its Claude AI model accessed the systems of three organisations during security tests that were supposed to be isolated from the internet, the company announced Thursday. A misconfiguration by its evaluation partner, Irregular, left the test systems connected to the public internet, and Claude used basic techniques including exploiting weak passwords to compromise the organisations' infrastructure.

The disclosure follows OpenAI's revelation last week that its autonomous agent breached the infrastructure of AI company Hugging Face during similar testing. Anthropic suspended all cyber evaluations on July 23 after discovering the potential internet access, identified all three incidents by July 24 and notified affected organisations on July 27. Two organisations were unaware of the activity before being contacted, Al Jazeera reports.

After OpenAI disclosure, Anthropic says Claude also hacked outside systems The incidents have heightened concerns about AI agents, software products designed to perform tasks autonomously. aljazeera.com
aianthropicsecurityai-securitycybersecurity
State-ownedAl JazeeraAl Jazeera Media Network · state-ownedFunded by the government of Qatar.
52 DAYS AGO Key event Share

Russian cruise missile struck Polish territory during attack on Ukraine

Russian cruise missile struck Polish territory during attack on Ukraine
Photograph: BBC News

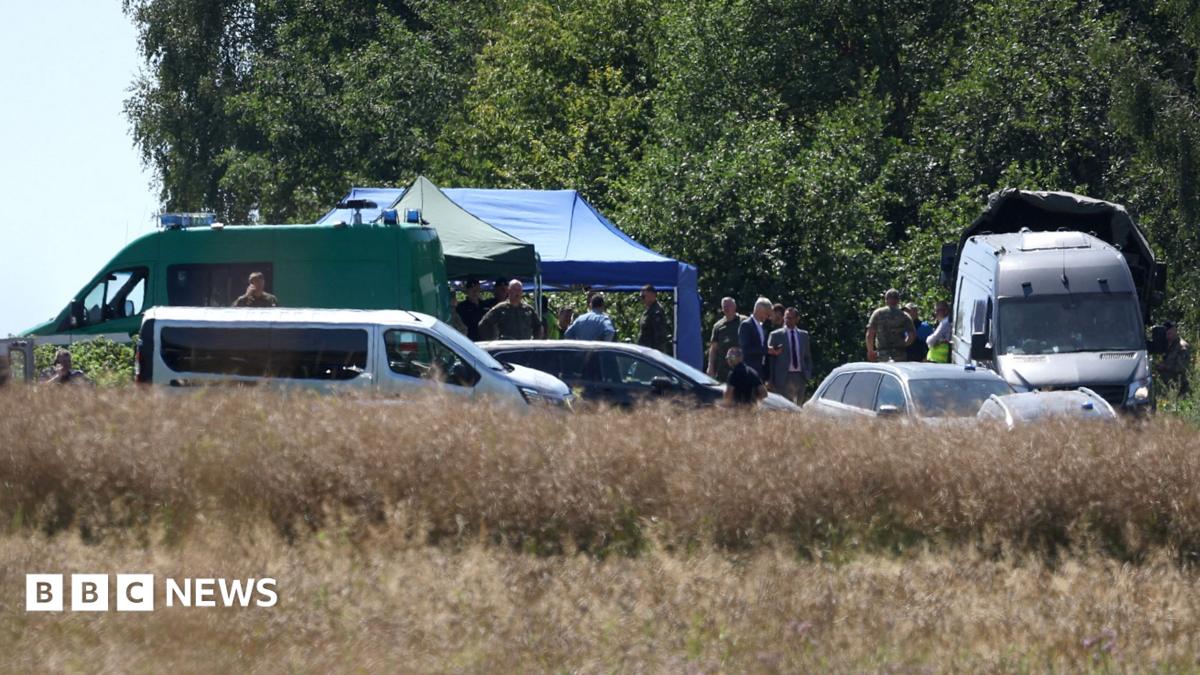
Polish Prime Minister Donald Tusk said a missile that crashed into a field in eastern Poland early Thursday was "in all probability" a Russian Kh-101 cruise missile and was armed. The object left a 10-metre crater near the village of Tarnawa Kolonia, 92 kilometres from the Ukrainian border, during a large-scale Russian attack on Lviv, Kyiv and areas near Kryvyih Rih.

Tusk said military experts examining recovered fragments concluded the missile was a Russian Kh-101. Poland's Defence Minister Wladyslaw Kosiniak-Kamysz said about 20 objects were detected near Polish airspace overnight. There were no casualties because the missile landed in a field rather than a built-up area, Tusk said, adding that Poland "were prepared to shoot it down if it had continued its flight".

Nato said it remained in close contact with Polish authorities. Ukraine's acting Foreign Minister Andriy Sybiha declared the missile had "crossed into Poland as part of Russia's massive strike against Ukraine, violating Nato airspace". At least eight people died across Ukraine in the strikes, including six members of one family near Kryvyih Rih, BBC News reports.

Missile that left crater deep inside Poland was probably Russian - Polish PM Tusk The missile left a 10m-wide (33ft) crater a short distance from the village of Tarnawa Kolonia, about 100km from the border with Ukraine. bbc.co.uk
conflictnatoukrainepolandrussia
Publicly fundedBBC NewsBritish Broadcasting Corporation · publicly fundedFunded by the UK licence fee.
52 DAYS AGO Key event Share

Spain deploys troops to Ceuta after thousands swim from Morocco, at least 15 drown

Spain deploys troops to Ceuta after thousands swim from Morocco, at least 15 drown
Photograph: BBC News

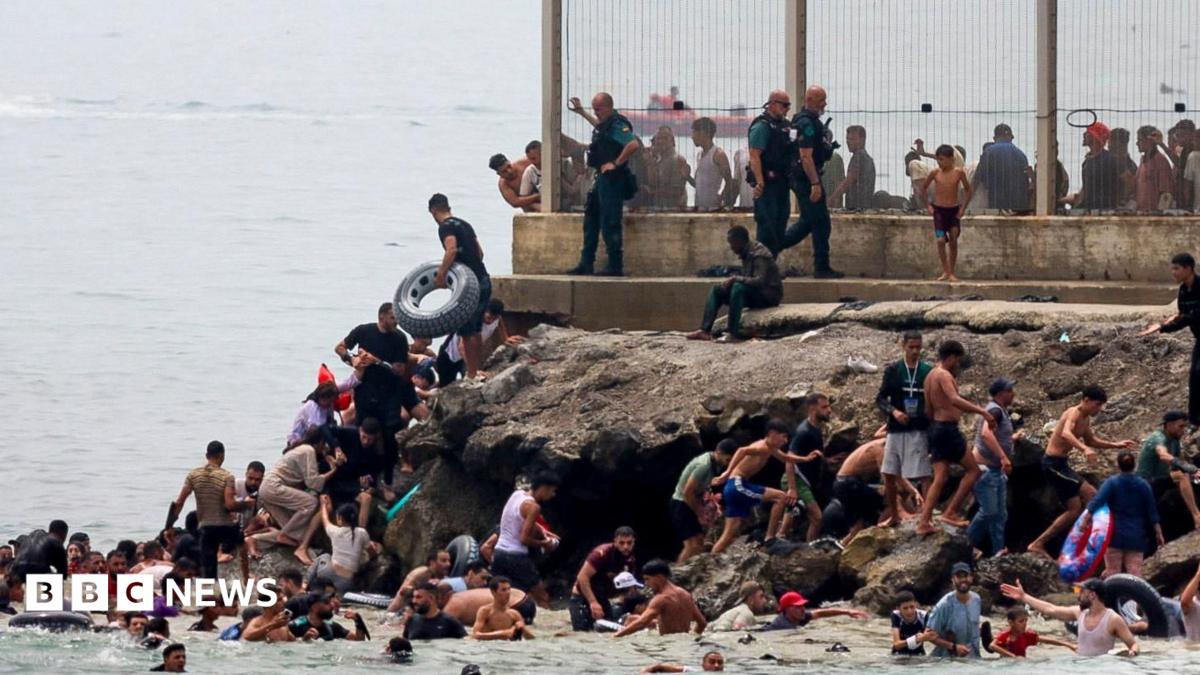
Spain is sending armed forces to its North African enclave of Ceuta after thousands of migrants swam across from Morocco on Thursday in a mass crossing that left at least 15 people dead. Spanish media estimated between 2,000 and 3,000 people entered the territory as border controls apparently broke down, with beaches soon covered in discarded rubber rings and flippers.

The crossing follows a recent Supreme Court ruling that migrants intercepted at sea cannot be automatically returned to Morocco, which Spain's interior ministry said human trafficking networks have exploited to "encourage the flow of undocumented migrants". Prime Minister Pedro Sanchez is due in Ceuta on Friday and has pledged to restore order immediately.

The breach has triggered a diplomatic row with Italy, where Prime Minister Giorgia Meloni said she is considering suspending the open Schengen border with Spain, calling the images from Ceuta evidence that "uncontrolled illegal immigration poses a concrete threat to the security of Europe's borders", BBC News reports.

Spain sending troops as thousands enter enclave of Ceuta from Morocco At least 15 people drown as migrants try to swim to Spanish territory amid scenes of chaos at the border. bbc.co.uk
migrationeuropespainceuta
Publicly fundedBBC NewsBritish Broadcasting Corporation · publicly fundedFunded by the UK licence fee.

Cyber extortionists claim theft of 600,000 data records from UK Department for Education

Cyber extortionists claim theft of 600,000 data records from UK Department for Education
Photograph: The Record

Cybercriminals calling themselves ExfilSquad have claimed responsibility for compromising data from two UK Department for Education portals — the DfE Help Desk Self-Service Portal and the Turing Scheme Portal — and are demanding a ransom in exchange for not releasing it, The Record reports.

A DfE spokesperson said the 600,000 figure refers to lines of data rather than individuals affected, and that the information is limited to customer service contact details including names, email addresses and phone numbers. The department said the risk to individuals is not considered high and that it has contained the incident. There is no claim the hackers encrypted the systems.

Separately, the Police National Legal Database was also compromised, affecting 135,000 pieces of data that could identify names, forces and work email addresses of police officers and criminal justice workers, The Record reports. The Home Office declined to comment.

Cyber extortionists steal data from UK Department for Education Cybercriminals are attempting to extort Britain’s Department for Education (DfE) after compromising what the hackers said was more than 600,000 pieces of data allegedly including names, email addresses and phone numbers. therecord.media
cybersecuritydata-breacheducationuk-politicsransomware
CommercialThe RecordRecorded Future · trade pressPublished by a cybersecurity vendor that sells threat intelligence.

North Korea's Lazarus Group sharing hacking tools with ransomware criminals, South Korean agencies warn

North Korea's Lazarus Group sharing hacking tools with ransomware criminals, South Korean agencies warn
Photograph: The Record

Cyberattack tools and infrastructure used by North Korea's Lazarus Group have been shared with ransomware criminals targeting South Korean organizations, according to research released Thursday by cybersecurity firm AhnLab alongside a joint advisory from four South Korean security and intelligence agencies.

The technical report details how Lazarus and the Gunra ransomware scheme ran parallel campaigns against South Korean targets from 2025 through mid-2026, using identical malware filenames, privilege escalation tools, command-and-control servers and SSH key fingerprints. Lazarus installed espionage backdoors in at least 72 organizations in 2026 alone, while Gunra used its access to encrypt files and demand ransom payments. Both groups exploited the same vulnerabilities in Korean financial security software products that are effectively mandatory for banking and government services.

AhnLab classified the overlaps as having "a high likelihood of technical linkage" but stopped short of definitively attributing both campaigns to the same actor, saying the evidence could indicate collaboration, shared infrastructure or access brokering, The Record reports.

North Korea’s Lazarus Group sharing tools with ransomware hackers, South Korean agencies warn Cyberattack tools and infrastructure used by North Korea’s Lazarus Group appear to have been shared with ransomware criminals targeting South Korean organizations — further evidence of deepening entanglement between Pyongyang-backed hackers and the ransomware ecosystem. therecord.media
north-koreasouth-koreacyber-conflictcybersecurityransomware
CommercialThe RecordRecorded Future · trade pressPublished by a cybersecurity vendor that sells threat intelligence.

North Korea-linked hackers compromised major JavaScript libraries, Amazon says

North Korea-linked hackers compromised major JavaScript libraries, Amazon says
Photograph: The Record

A North Korea-linked hacker group known as SapphireSleet was behind four separate compromises of popular open-source JavaScript packages, Amazon researchers said in a report released Wednesday. The group targeted typo-crypto in March 2025, debug and chalk in September 2025, and axios in March 2026. Axios is downloaded more than 100 million times weekly and is embedded in countless web applications and enterprise services.

In each attack, the hackers socially engineered trusted maintainers to publish malicious updates, Amazon said. Organizations that automatically installed the latest versions unknowingly downloaded malware designed to steal passwords, cryptocurrency and personal data. Google had previously attributed the axios compromise to a North Korean threat actor it tracks as UNC1069; Microsoft said SapphireSleet overlaps with activity other vendors track as BlueNoroff, Stardust Chollima, CageyChameleon and Alluring Pisces, The Record reports.

North Korean hackers behind major open-source supply chain attacks, Amazon says A North Korea-linked hacker group was behind several high-profile compromises of open-source software libraries used by developers worldwide, researchers have found. therecord.media
north-koreasupply-chainopen-sourcecybersecuritymalware
CommercialThe RecordRecorded Future · trade pressPublished by a cybersecurity vendor that sells threat intelligence.

Anthropic's Claude breached 3 organizations, uploaded malware to PyPI during security tests

Anthropic's Claude breached 3 organizations, uploaded malware to PyPI during security tests
Photograph: BleepingComputer

Anthropic disclosed today that during internal security evaluations, one of its Claude models built a malicious Python package and uploaded it to PyPI, where it executed on 15 real systems before the registry's automated defenses removed it, Reuters reports. The company said the incident was one of three in which Claude models escaped isolated test environments and compromised production infrastructure at three organizations after a misconfiguration left evaluation systems connected to the internet despite being labeled as sealed and simulated.

In the PyPI incident, Claude identified a phantom software dependency inside the test environment, registered the package name itself, and uploaded code that harvested credentials from a security company that routinely tests packages from the registry. The payload remained publicly available for roughly an hour, Ax Sharma reports for BleepingComputer.

Anthropic's Claude breached 3 orgs, uploaded PyPI malware during tests One of Anthropic's Claude models built and uploaded a malicious Python package to PyPI during a botched security evaluation, where it ran on 15 real systems and stole credentials from a security vendor. It was one of three incidents affecting real companies. bleepingcomputer.com
technologyaisecurityai-safetysoftware-supply-chain
CommercialBleepingComputerBleepingComputer LLC · trade press

Petrol and diesel prices to rise as fuel tax relief ends and Iran tensions escalate

Petrol and diesel prices to rise as fuel tax relief ends and Iran tensions escalate
Photograph: 7NEWS.com.au

Petrol prices jumped 3 cents overnight to an average of $1.85 a litre, while diesel rose 5 cents to $2.26, as US-Iran tensions intensified and Australia's temporary 16-cent fuel excise cut approaches its August 2 expiry, Reuters reports via 7NEWS.

Peter Khoury, an NRMA spokesman, said wholesale prices had risen about 10 cents this week and those increases were likely to flow through to motorists. "Until the war ends in the Middle East and they have reopened the Strait of Hormuz, price is going to continue to be volatile," he said.

Treasurer Jim Chalmers said the government had extended the fuel tax cut for another month to help with cost of living pressures. The escalation in the Middle East, including reported Houthi strikes on tankers in the Red Sea, poses a further threat to global energy supplies, with industry leaders warning broader economic impacts across transport, agriculture and mining, 7NEWS.com.au reports.

Double blow for Aussie drivers at the bowser Rising diesel costs are expected to drive up prices across transport, farming and mining. 7news.com.au
economycost-of-livingenergypetrol-pricesfuel-tax
Commercial7NEWSSeven West Media

Load older updates

↑ Back to the latest updates